How often should a small SaaS run vulnerability scans? Compare SOC 2, ISO 27001, HIPAA and PCI DSS requirements, then set a cadence by environment and change rate.
Want hands-on SOC 2 or compliance help without signing a three-year contract? Here's who offers flexible terms, what each model costs and what to check in the contract.
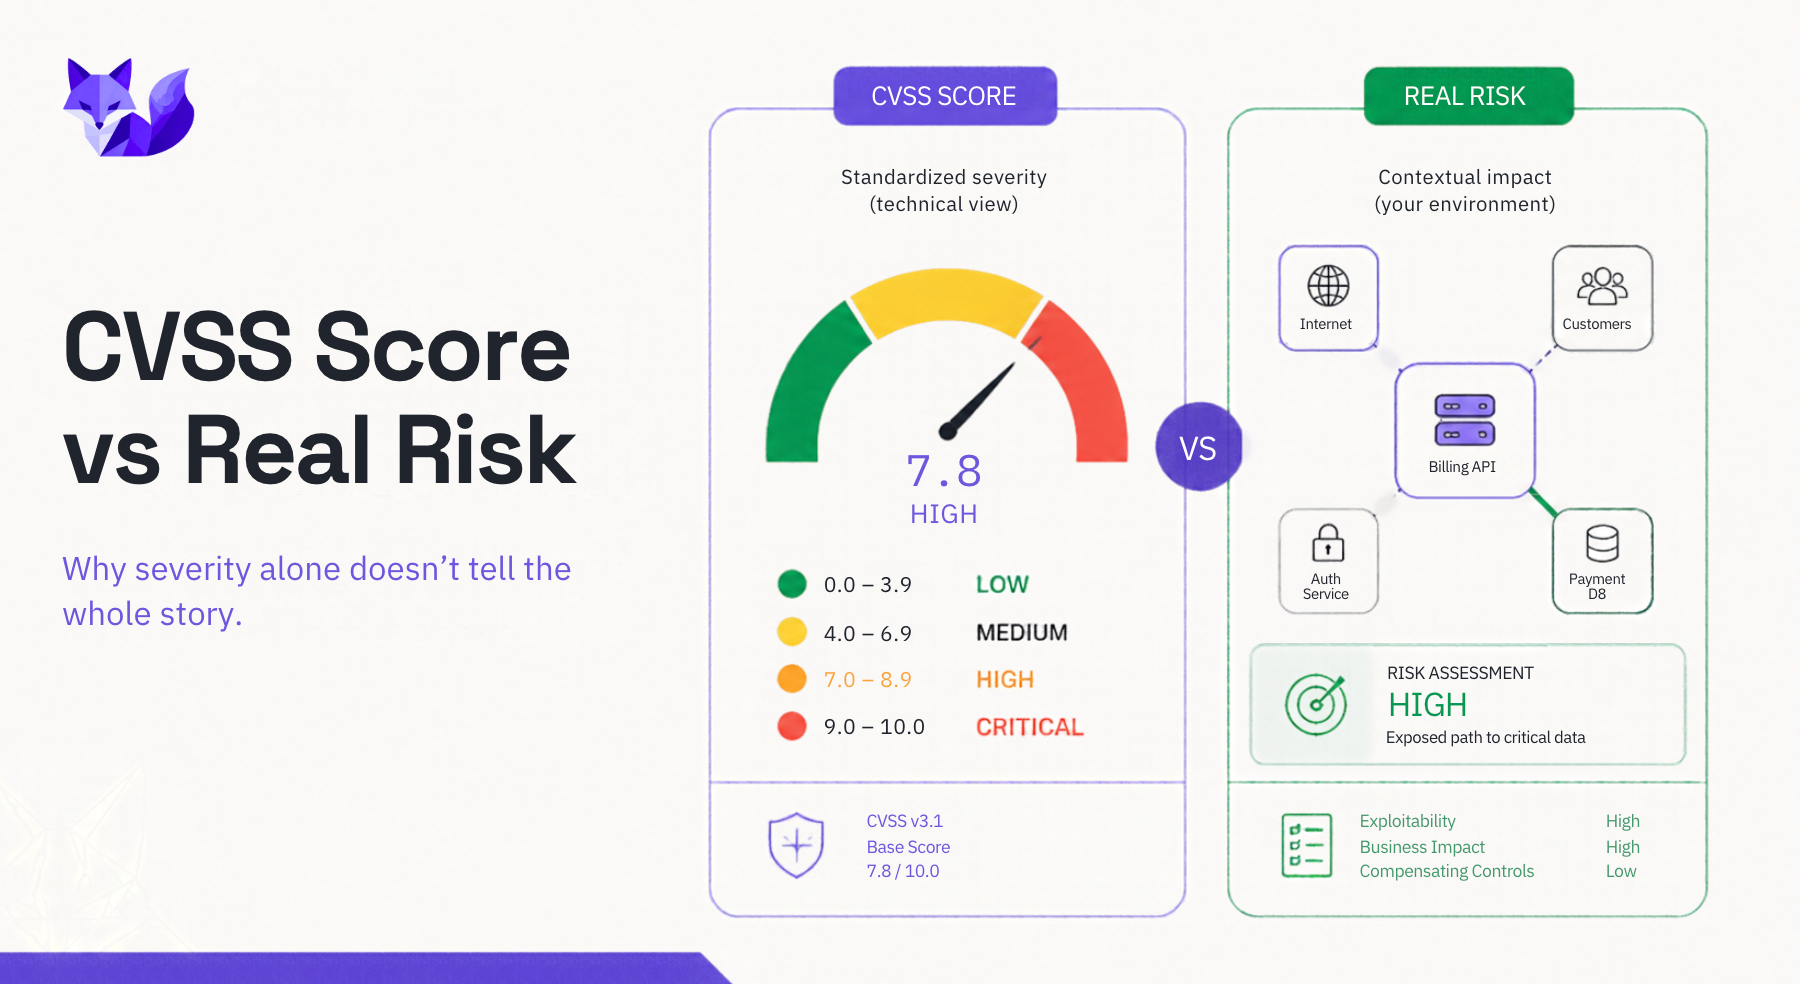
A CVSS 9.8 sounds terrifying, but severity and risk are different things. Learn how exploitability, exposure and compensating controls change what you fix first.
What does SOC 2 say about vulnerability scanning? We walk through CC7.1 and CC4.1, the evidence auditors ask for, and what "regular" scanning means in practice.
Need someone to do the SOC 2 prep work with you? Here's where to find hands-on help, what it costs and how to spot a provider who'll do the work.
Comparing SOC 2 readiness services for a small software company? See the main options, what they cost, what to look for and the red flags, in plain English.
Can't justify a full-time security hire yet? Compare a vCISO, managed security services and compliance platforms on cost, speed and reliability, with real 2026 pricing.
SOC 2 stats for 2026: what audits cost, how long they take, how many buyers require one, and how often deals stall without it. Sourced numbers, plain English.
SOC 2 Type I or Type II? See how long each takes, which one enterprise buyers accept, and the fastest way through procurement without paying for two audits.