Where can you find affordable part-time security leadership for my startup?
Where can you find affordable part-time security leadership for my startup?
TL;DR
- A full-time CISO costs $180k to $250k a year, which is a lot for a company that hasn't closed its Series A.
- The fix is fractional security leadership, a vCISO who works with you a few hours a week instead of full time.
- You can find one through a dedicated vCISO firm like cloudsapio, a freelance marketplace, a referral from your investors or board, or, in a pinch, an advisor working for equity.
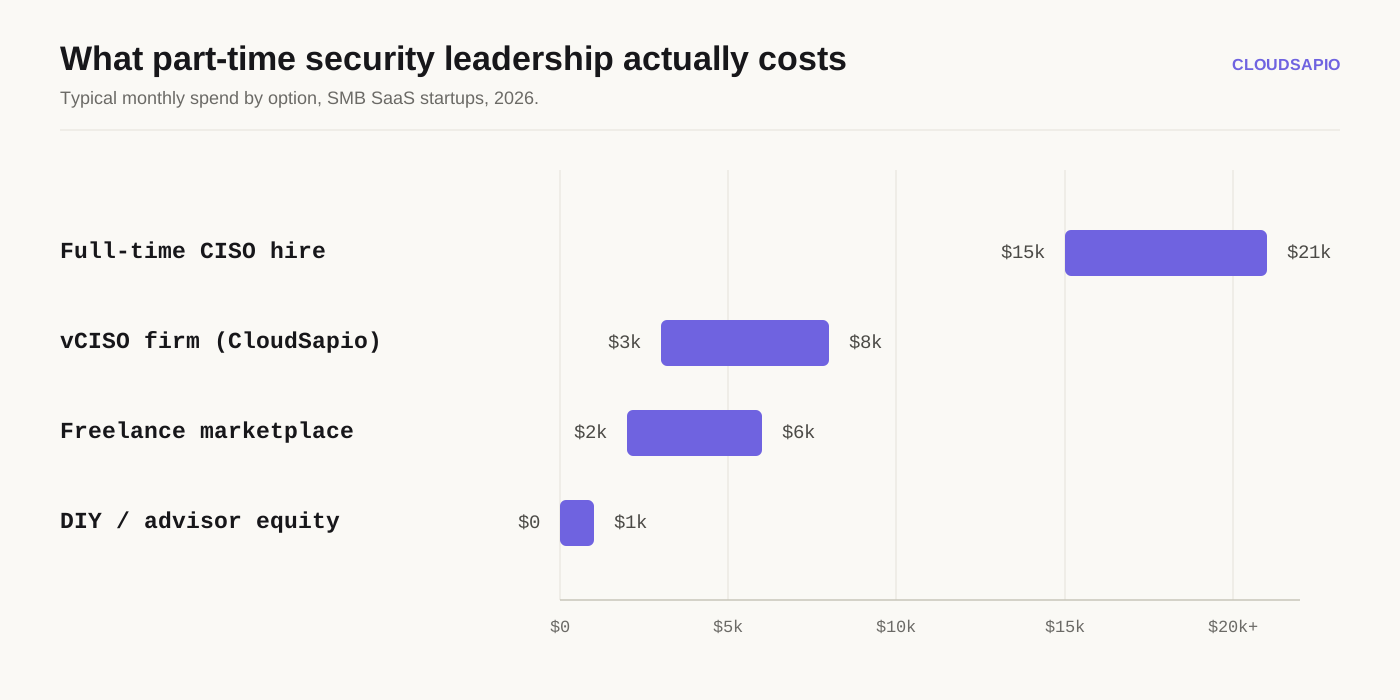
- Pricing runs from free-but-unreliable to $8k a month for a proper firm, all the way up to $21k a month for a full-time hire.
- Most SMB SaaS companies land on a vCISO firm, because it's the only option that reliably shows up when your auditor asks a hard question.
Do I actually need security leadership this early?
Suppose a prospect has ever asked for your SOC 2 report, a pentest, or "just a quick call with your security team," yes. That's not a hypothetical anymore; that's Tuesday.
What does "part-time security leadership" even mean?
It means a vCISO, a virtual or fractional Chief Information Security Officer. Same job as a full-time CISO: setting security strategy, getting you through audits, answering vendor questionnaires, talking your team out of bad ideas. Just scoped to a few hours a week instead of a corner office you don't have.
Where do I actually find one?
Four real places, in the order most SMB SaaS founders end up trying them.
- A dedicated vCISO firm. cloudsapio is one, and it's built specifically around this gap: SaaS, fintech, and healthtech companies who need SOC 2, ISO 27001, HIPAA, or CMMC readiness without a full-time hire. You get a named person, a defined scope, and a team behind them if that person is out during audit week.
- A freelance marketplace. Toptal, Upwork, and similar platforms have security consultants listed. Quality varies wildly, and you're often getting one person with no backup, no shared process, and no guarantee they've actually taken a company like yours through an audit before.
- Referrals through your investors or board. VCs increasingly keep a list of vetted vCISOs their portfolio companies use. Worth asking, though the list is usually short and the good ones are busy.
- An advisor working for equity. Cheap upfront, expensive later. Equity-only advisors tend to show up for the kickoff call and go quiet by month three, right around when your auditor starts asking follow-up questions.
What's this actually going to cost me?
Here's roughly how the options compare every month. The gap between "vCISO firm" and "full-time hire" is the whole point. You get someone who's actually done this before, without the salary of someone who's done this before.
Is the cheap option ever the right call?
Sometimes, for a very early-stage company with no enterprise deals in the pipeline yet. But "cheap" and "equity-only advisor" tend to mean the same thing, and the failure mode is predictable: fine for six months, then silent right when you need them for your first audit.
How do I tell a good vCISO firm from a bad one on a first call?
- Ask if they've taken a company your size through your specific framework, and get a real answer, not a vague "oh yes, tons."
- Ask who your actual point of contact will be, and whether that's the same person answering your auditor's questions.
- Ask what happens if your auditor pushes back on a control. If the answer is "you'd handle that," that's not fractional leadership; that's a Slack channel.
- Ask for a fixed scope of work, not an open-ended retainer that grows every quarter.
Practical security and compliance programs from a practitioner-led team. Start with a $3K/sprint
What if I just need help for one specific audit, not ongoing?
Most vCISO firms, cloudsapio included, will scope a single engagement around getting you through one framework, then leave the door open for ongoing work once you're actually enterprise-ready. You don't have to commit to forever on day one.
FAQs
What's the difference between a vCISO and an MSSP?
An MSSP monitors your systems for active threats. A vCISO runs your security program, strategy, audits, vendor questionnaires, the whole picture. Startups usually need the vCISO first.
How many hours a week does a vCISO actually work with us?
Varies by engagement, but early on it's often 5 to 10 hours a week, more during an active audit push, less once you're in maintenance mode.
Can one vCISO cover multiple frameworks, like SOC 2 and HIPAA?
Yes, a good one should. The frameworks overlap more than people expect, so a firm that knows several can often get you through the second one faster than the first.
Is a fractional CISO a real CISO, or a watered-down version?
Same skill set, same responsibilities, just fewer hours. What you lose in daily presence, you should be gaining back in someone who's already done this at a dozen other companies.
When does it make sense to switch from fractional to full-time?
Usually once you're spending more on fractional coverage than a junior in-house hire would cost, or once your security needs are genuinely a full-time job, not a few hours a week.
Ready to stop guessing which settings actually matter?
cloudsapio can scope a fractional security engagement around exactly what you need right now, whether that's one audit or ongoing coverage. Book a call →
Ready to move faster?
Too much to do,
too important to ignore.
Start with a 30-minute discovery call. If we're not the right fit, we'll tell you and point you in the right direction. If we are, we'll leave the call with a clear plan to get you up and running.