Vulnerability management
You've got your scan results.
Now what?
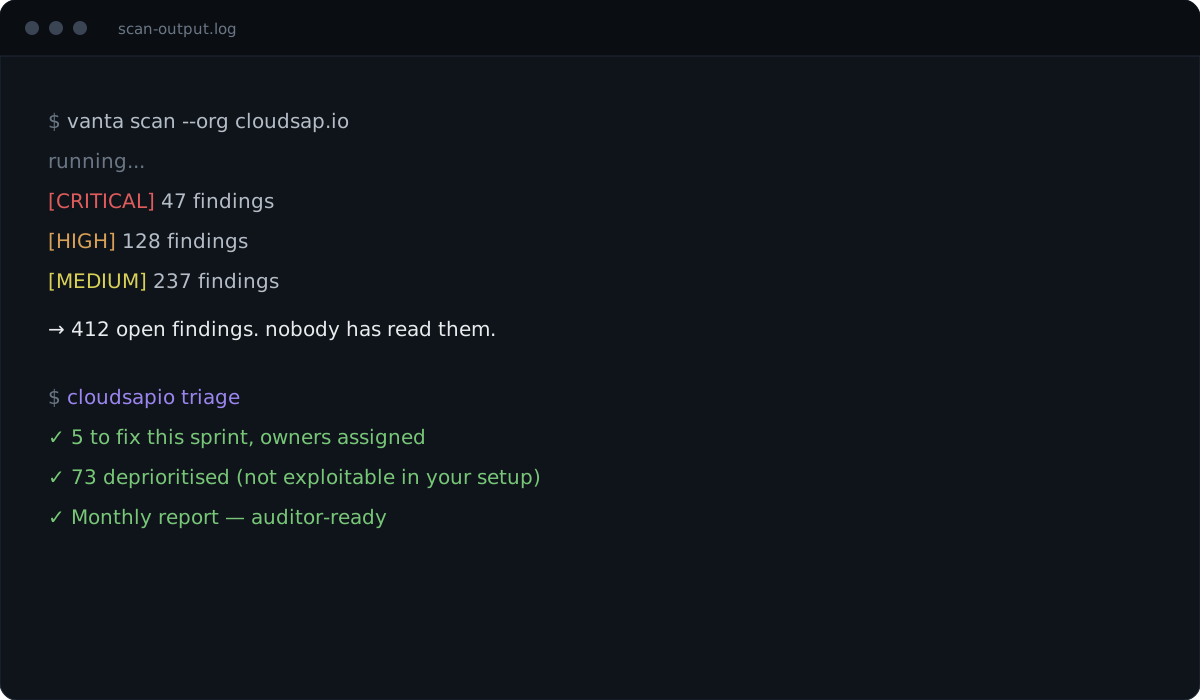
Vanta, Drata, AWS Inspector, and GitHub are all flagging issues for you: four hundred reds, no owners, no order.
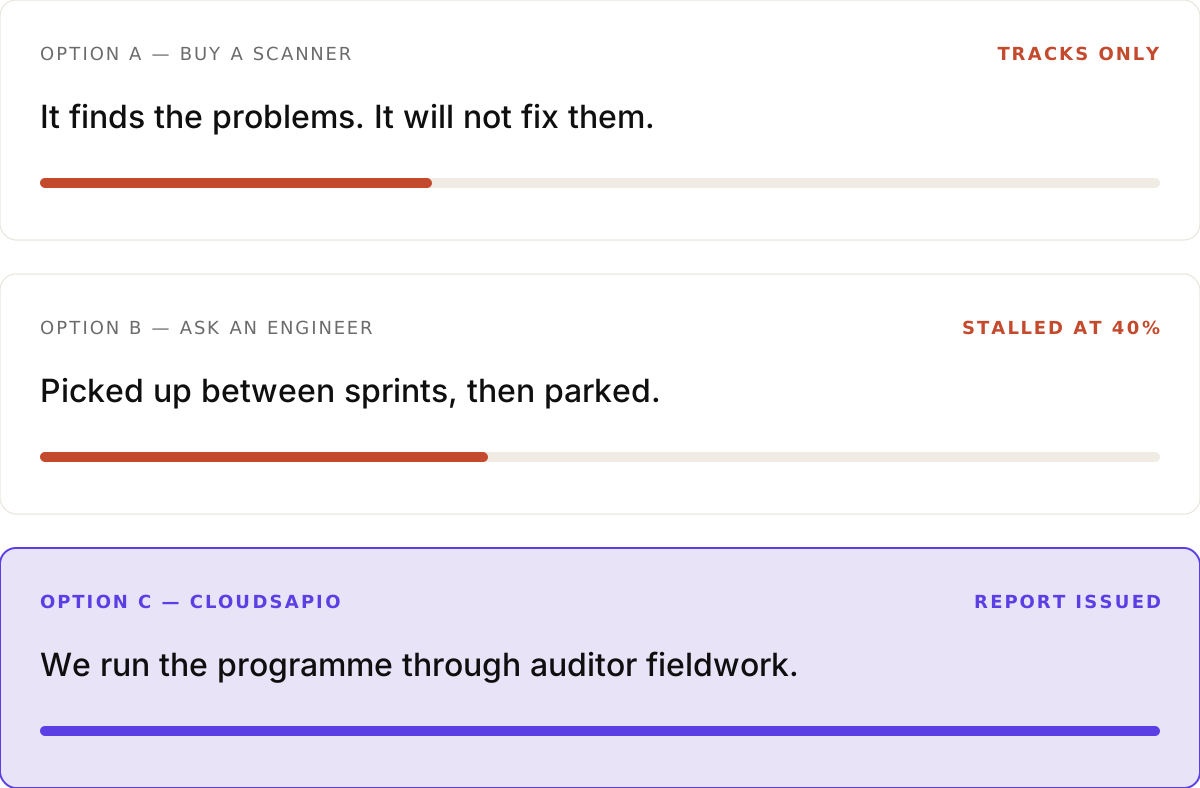
We read the output, tell you which five things matter this sprint, and give your auditor the evidence they want.
The problem
A scanner is not a program.
Scanning tools are a commodity now. Vanta and Drata include one. AWS gives you Inspector. Dependabot runs for free.
A busy founder opens the dashboard, sees 412 criticals, and closes the tab. The auditor comes back three months later asking why nothing was closed.
The customer sends a questionnaire asking what your remediation SLAs are, and nobody has an answer.
The translation
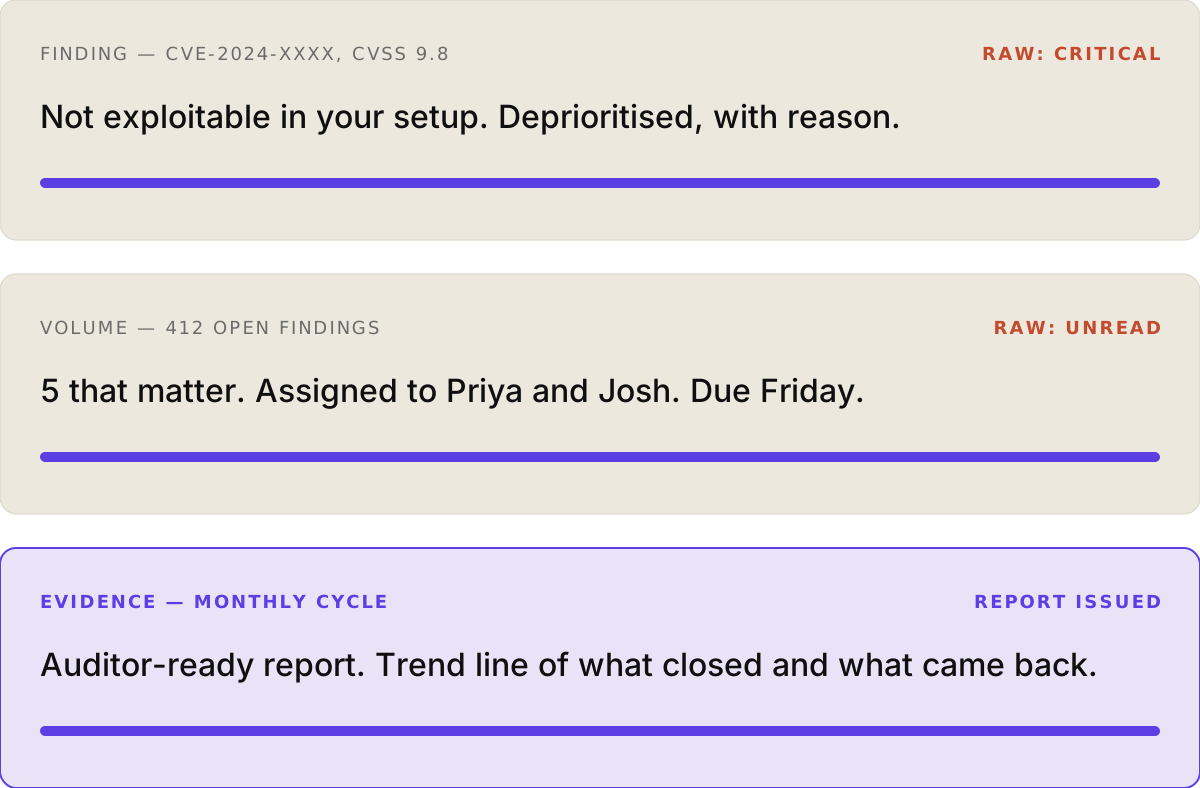
The scanner tells you
what. We tell you
what to do.
Three things change the moment we take over the output.
WHAT YOU GET
Deliverables
Authenticated internal and external scans on a recurring schedule, covering cloud, network, and web application surfaces.
01
Scope and asset inventory confirmation
02
Authenticated and external scans across network, cloud, and web application surfaces
03
Triaged findings with CVSS scoring and exploitability context
04
Cross-reference against your asset inventory to cut false positives
05
Remediation priority with recommended owners
06
Trend reporting across scan cycles, showing what closed and what recurred
HOW IT WORKS
The engagement step-by-step
01
Discovery call (30 min)
What your framework requires, what you already scan, and what your environment looks like.
02
Scoping
We confirm the asset inventory, the external footprint, and the credentials needed for authenticated scanning. You get a fixed scope and price before anything runs.
03
Baseline scan
The first cycle usually produces the largest finding count. We triage it fully so you start with a real picture rather than a backlog.
04
Triage and report
Findings are deduplicated, scored, checked against your architecture for exploitability, and ordered by what actually matters. Each one gets a recommended owner.
05
Remediation support
We work with your engineers on the fixes that need context, and retest to confirm closure.
06
Ongoing
Subsequent scans run on the agreed cadence with trend reporting, so you can show your auditor the programme is operating rather than that a tool exists.
The questions that come up on every first call.
-
How is this different from penetration testing?
Scanning is broad, automated, and recurring. It finds known vulnerabilities across your whole estate. A penetration test is a person attempting to chain weaknesses into a real attack path, scoped to a target and run occasionally. Most frameworks expect scanning continuously and a pentest annually. They answer different questions and neither replaces the other.
-
How often do we need to scan?
Depends on your framework and how fast your environment changes. Quarterly is a common floor for audit purposes; monthly suits teams shipping frequently or running significant internet-facing infrastructure. We recommend a cadence on the first call.
-
What does authenticating scanning means?
An authenticated scan logs into the system with credentials and sees what is actually installed, rather than inferring from the outside. It finds substantially more and produces far fewer false positives. Most auditors expect it for internal systems.
-
Will this disrupt production?
Standard scanning is non-intrusive and we schedule it around your operations. We agree any potentially disruptive checks with you before they run.
-
Does this satisfy our SOC 2 or ISO 27001 requirement?
The scanning does, provided the findings get triaged and closed and you can evidence it. That last part is where most programmes fail an audit, and it is why every cycle here ends with packaged evidence rather than a raw export.
RELATED CAPABILITIES
Ready to move faster?
Too much to do,
too important to ignore.
Start with a 30-minute discovery call. If we're not the right fit, we'll tell you and point you in the right direction. If we are, we'll leave the call with a clear plan to get you up and running.