compliance Framework
Frameworks
SOC 2, ISO 27001, HIPAA, and CMMC — assessed, built, remediated, and audited by one team.
DELIVERED THROUGH
A Cloudsapio vCISO engagement
engagement levels
Advisor · Consultant · Leader
frameworks
SOC 2 • ISO 27001 • HIPAA • CMMC
THE FRAMEWORKS
Which one you need is usually decided by
your customer
Most companies do not choose a framework. A buyer, investor, or contracting officer asks for one, and the deal waits until you have it. Here is what each one is and who asks for it.
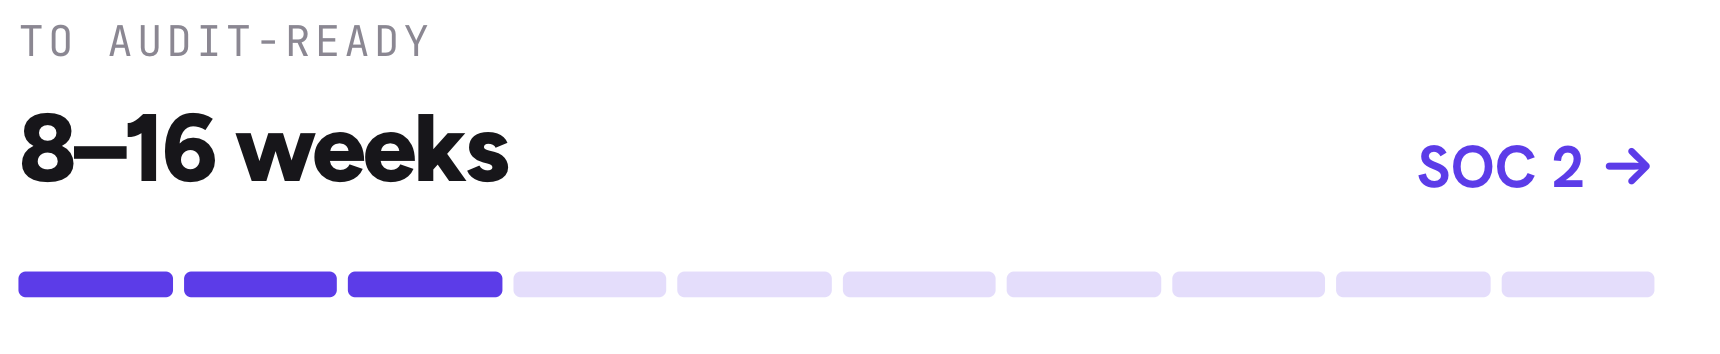
What US buyers ask for. An independent CPA firm reports on your controls, either at a point in time (Type I) or over a period (Type II).
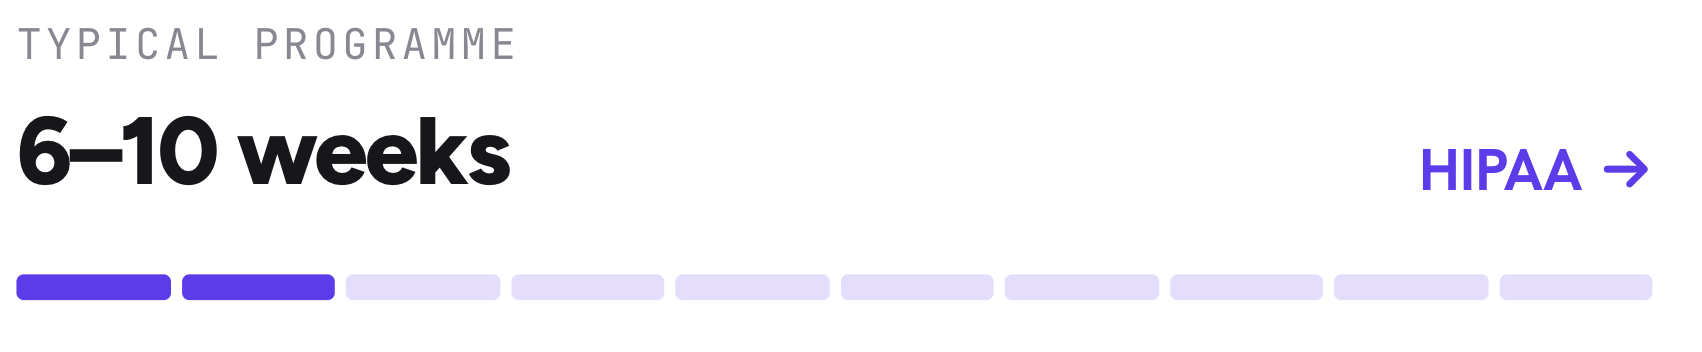
A legal obligation, not a certificate, if you handle Protected Health Information for a healthcare customer. What you need is a defensible programme: risk analysis, safeguards, BAAs, breach procedures.

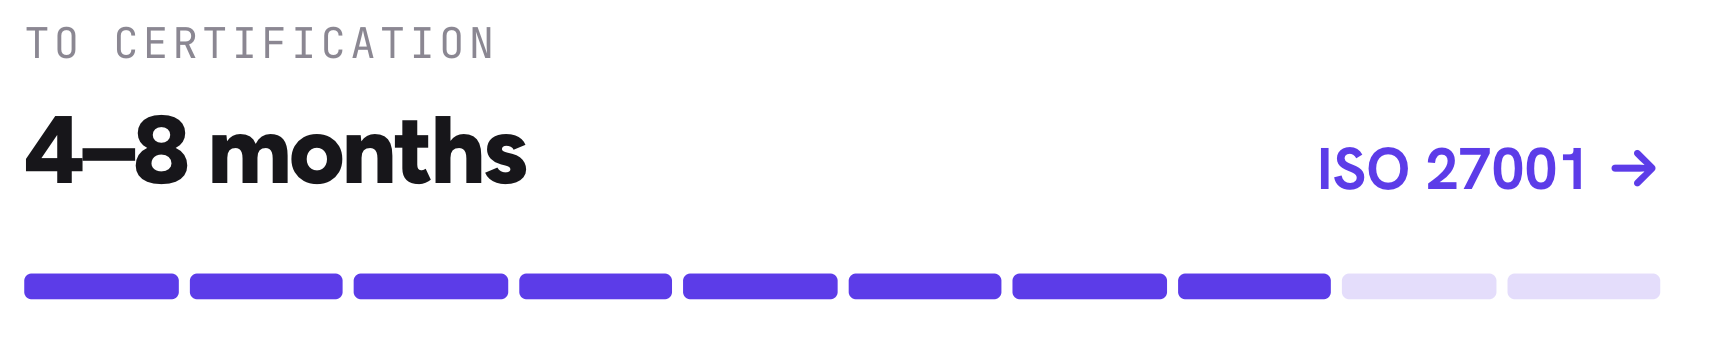
What UK, EU, and most international buyers ask for. An accredited body certifies your information security management system across two audit stages.

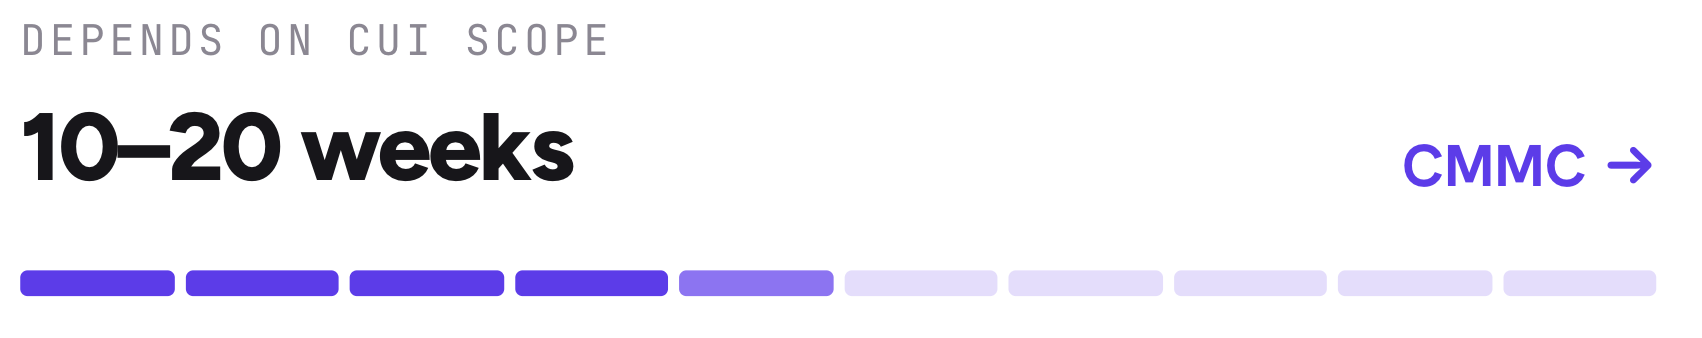
Required for defence work. NIST 800-171 control coverage, System Security Plan, POA&M, and a SPRS score you can defend.

how cloudsapio helps
We do the work, you approve the decisions
Most compliance offerings fall into one of two categories. Platforms track the work but do not do it. Auditors tell you what is wrong but cannot fix it, because independence rules prevent them. Both leave the actual programme with you.
A CloudSapio vCISO runs your programme end to end.
01
Assessment
We review your controls, environment, and documentation against the framework and tell you where you actually stand.
02
Documentation
We write the policies, procedures, risk registers, and plans. You review and sign rather than draft.
03
Remediation
Your engineers get specific tasks, not control descriptions to interpret. We work alongside them.
04
Evidence
We collect and organise what the assessor will ask for, in your compliance platform or ours.
05
Audit support
We manage the assessor, respond to findings, and stay on until the report, certificate, or score is issued.
06
Ongoing
Every framework has continuing obligations. We can run them for you or hand over documented processes and a calendar.
WHAT YOU CAN EXPECT FROM US
Fixed scope and price before work starts
A named person who stays on your engagement
Roughly an hour a week of your time
A straight answer if we are not the right fit
how to start
Three steps
Step 01
Book a 30-minute discovery call
Tell us who asked, what they asked for, and when they need it. We tell you which framework applies, what it will take, and roughly what it costs.
Step 02
Get a scoped proposal
Within a few days you get a fixed scope, timeline, and price. No open-ended hours.
Step 03
Kick off
We start with the assessment and you have a roadmap in the first few weeks.
Ready to move faster?
Too much to do,
too important to ignore.
Start with a 30-minute discovery call. If we're not the right fit, we'll tell you and point you in the right direction. If we are, we'll leave the call with a clear plan to get you up and running.