SOC 2 in Stats: Costs, Timelines and Who Requires It
SOC 2 in Stats: Costs, Timelines and Who Requires It
TL;DR
- Cost: A 50 to 100 person SaaS company should budget $50,000 to $110,000 for its first Type II with a compliance platform, and $78,000 to $170,000+ without one. The audit fee is usually less than half of that.
- Time: Readiness takes about 6 to 8 weeks. The Type II observation window runs 3 to 12 months, and 6 months is the most common for a first audit.
- Who requires it: 61% of companies surveyed by Secureframe said compliance was required to win or renew a contract. 71% of ISC2 respondents require security audits or attestations from vendors.
- What it costs you to skip it: 47% said a lack of certification delayed their sales cycle, and 38% said it cost them revenue or a bid.
- It doesn't end the paperwork: 68% of buyers still ask for more documents after getting your SOC 2 report.
Every SOC 2 vendor has a blog post telling you SOC 2 costs "it depends" and takes "a few months." That's accurate, and you can't put it in a budget.
So we gathered the numbers: published price ranges, benchmark studies and buyer surveys. Each stat says where it came from, because a stats post with no sources is just a list of vibes.
How much does SOC 2 cost?
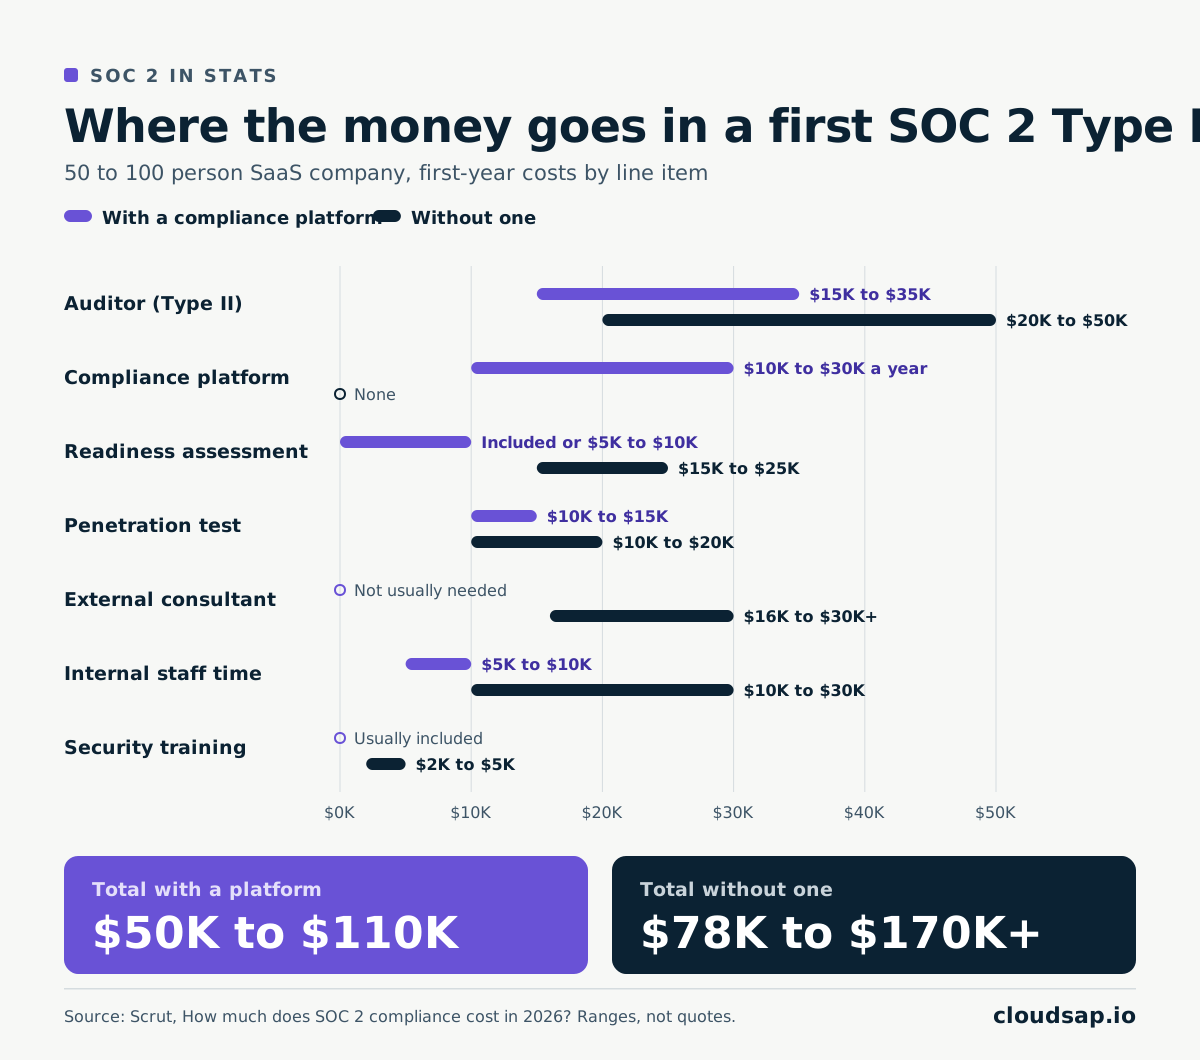
For a 50 to 100 person SaaS company doing its first Type II, Scrut's breakdown puts the total at
$50,000 to $110,000 with a compliance automation platform, and $78,000 to $170,000+ without one. Here's where the money goes:
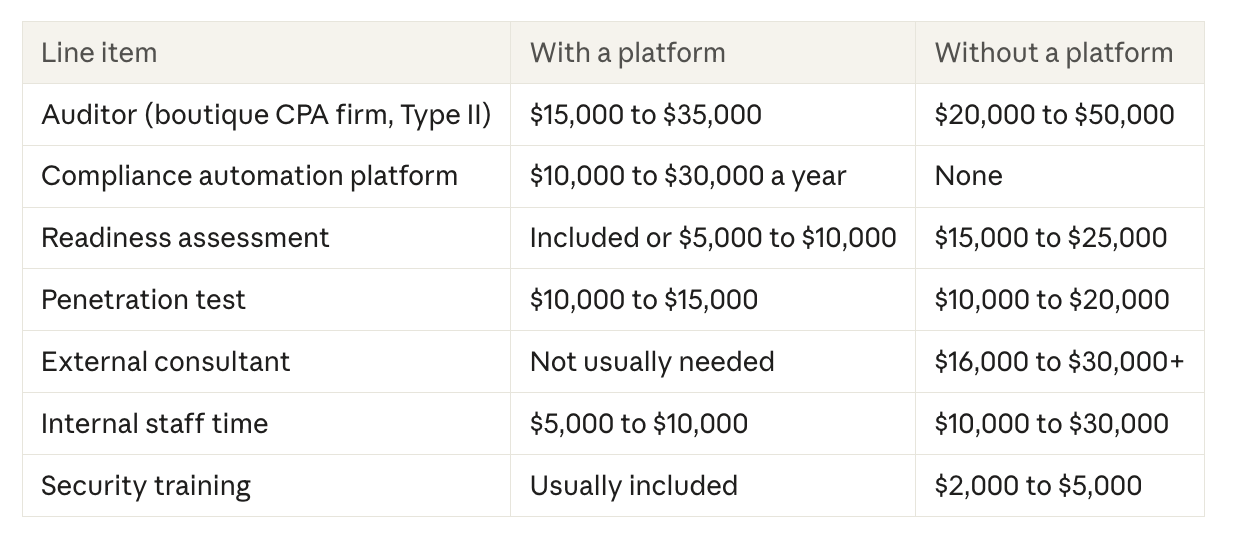
What about the audit fee alone? Published guides don't agree. Drata's cost guide puts Type I at $7,500 to $15,000 and Type II at $12,000 to $20,000 for small and midsize companies. The same guide puts Type II at $30,000 to $100,000+ for large organizations. Hire a Big Four firm and Scrut says a 100-person company should expect $50,000 or more for the assessment alone. You can choose the firm with the nicest lobby, but your CFO will find out what it cost.
The second year is cheaper. Agency estimates renewal costs at 20% to 40% less than year one, since the policies, tools and evidence already exist.
What costs do people forget to budget for?
The auditor's invoice is the easy part to plan for. These are the costs that show up later:
- Engineering time. Someone has to turn on logging, set up MFA, fix access permissions and gather evidence. Scrut calls it a hidden cost and doesn't put a number on it. Ask your CTO how many sprints "SOC 2 stuff" used last year.
- Device management. Scrut lists an MDM tool at $5,000 to $10,000. You need one, because "we trust everyone to update their laptops" won't satisfy the auditor.
- Remediation. Fixing a failed control can cost anywhere from $10,000 to millions, depending on what failed.
- Every year after. Without automation, Scrut puts yearly maintenance and re-audits at $20,000 to $50,000. SOC 2 renews every year, like a gym membership you actually have to use.
It helps to compare these numbers with the cost of a breach. IBM's 2024 report put the global average at $4.88 million, which makes a $60,000 audit look cheap.
How long does SOC 2 take?
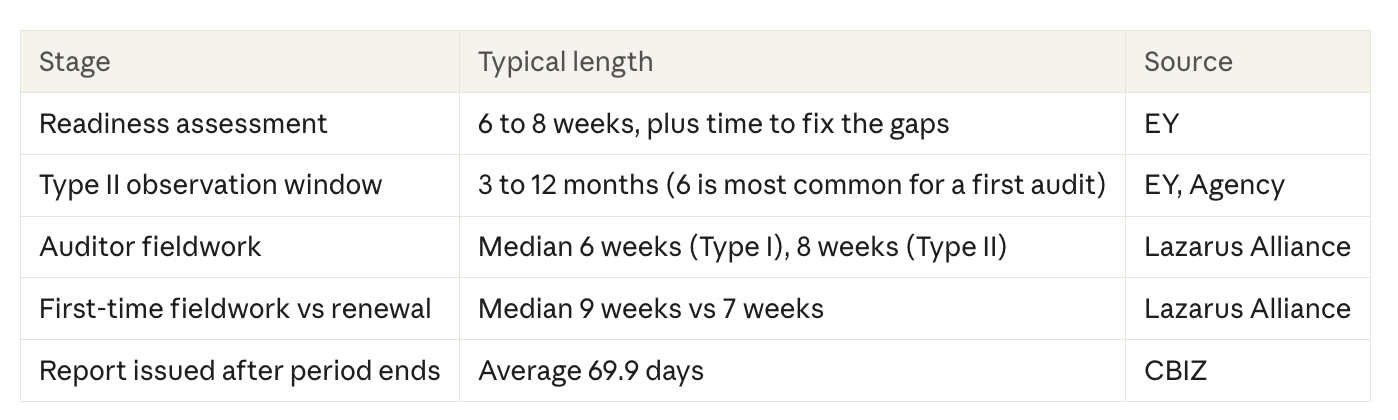
In short: plan on 6 to 14 months from kickoff to your first Type II report. Here's how that time breaks down, from the benchmarks collected by Bright Defense:
Who requires SOC 2?
Short version: enough buyers that you'll probably need one. Here's what the surveys say, again via Bright Defense:
- 77% of ISC2's 2025 Supply Chain Risk Survey respondents list compliance with standards such as SOC 2, ISO 27001, or NIST among their vendor security requirements.
- 73% of companies in a Secureframe survey regularly need to share a third-party audit report such as SOC 2.
- 71% of ISC2 respondents require vendors to provide security audits, attestations or assessments.
- 61% of respondents to Secureframe's 2026 benchmark report said compliance was required to win or renew a contract.
- 51% of in-house lawyers in the Association of Corporate Counsel's 2025 survey ask vendors for proof of certification, with SOC 2 and ISO 27001 as examples.
None of these measure SOC 2 alone, which is worth knowing when you see a confident "X% of enterprises require SOC 2" on someone's homepage. Most surveys group SOC 2 with ISO 27001 and similar frameworks.
Where you sell matters too. Drata's platform data for the first half of 2026 shows SOC 2 enabled on 76% of accounts in the Americas, compared with 52% in Europe, the Middle East and Africa, where ISO 27001 is more common.
What happens when you don't have one?
The deal usually still happens, just later or with someone else. From Secureframe's research:
- 47% said a lack of certification delayed their sales cycle.
- 38% said they lost revenue or a competitive bid because they didn't have it.
- 40% said they pursued formal compliance specifically to reach enterprise buyers.
Getting the report won't end the paperwork either. 70% of companies still rely heavily on security questionnaires, and Whistic found 68% of buyers are likely to ask for more documents after receiving a vendor's SOC 2 or ISO 27001 report. The good news is that most answers on a security questionnaire become "see section 4 of our SOC 2 report."
FAQs
What is the cheapest way to get SOC 2? A boutique CPA firm, a compliance automation platform, and a Type I first if your buyers will accept one. Cheap auditors exist, but a report from a firm your buyer has never heard of may lead to more questions.
Is a compliance automation platform worth it? Scrut's numbers suggest it usually is for a first audit. The platform costs $10,000 to $30,000 a year, and in their example it lowers the total by more than that by cutting consultant and staff time.
How much does SOC 2 cost in the UK? Scrut puts auditor fees at £4,000 to £20,000 for Type I and £12,000 to £40,000 for Type II.
Do I need a penetration test for SOC 2? SOC 2 doesn't strictly require one, but most auditors and buyers expect it. Budget $10,000 to $20,000 for a mid-size SaaS product.
How long does the report stay valid? There's no official expiry. Buyers generally want a report covering a period that ended in the last 12 months, so plan for a yearly cycle.
Why do the numbers vary so much between sources? Most published ranges come from vendors and auditors pricing their own services, and few come from surveys of what companies actually paid. Treat them as budgeting ranges, and get two or three quotes.
Want your own numbers instead of industry ranges?
Book a free 45-minute gap analysis with cloudsapio. We'll look at where you are today and give you a realistic estimate of what SOC 2 will cost you and when you'll have a report to show buyers.
Ready to move faster?
Too much to do,
too important to ignore.
Start with a 30-minute discovery call. If we're not the right fit, we'll tell you and point you in the right direction. If we are, we'll leave the call with a clear plan to get you up and running.